The California Court of Appeal, Second Appellate District, has issued its tentative ruling in Variety Media, LLC v. Superior Court, the closely watched writ proceeding that asks whether the pen register provisions of the California Invasion of Privacy Act (“CIPA”) apply to common website tracking technologies. The tentative decision would grant Variety’s petition in part and direct the trial court to sustain Variety’s demurrer with leave to amend. The court’s reasoning cuts in both directions. The panel would hold that CIPA’s pen register statute reaches internet communications, rejecting the threshold defense that has anchored many motions to dismiss. But it would also hold that a pen register captures only metadata identifying the destination of an outgoing communication, and that a website visitor’s IP address identifies the source of a communication rather than its destination. Under that construction, the complaint before the court fails to state a claim.

Background

Penal Code section 638.51 prohibits installing or using a pen register without a court order or the user’s consent. Over the past three years, plaintiffs and pro se litigants have filed hundreds (if not thousands) of lawsuits, arbitration demands, and pre-suit letters alleging that cookies, pixels, analytics tools, and similar technologies are unlawful pen registers because they collect visitors’ IP addresses and device information. Trial courts have divided on whether the statute, enacted with telephone surveillance in mind, reaches these tools at all. No California appellate court has answered the question in a published decision.

Continue Reading California Court of Appeal Tentatively Holds That Collecting a Website Visitor’s IP Address Alone Does Not Constitute Pen Register Activity Under CIPA
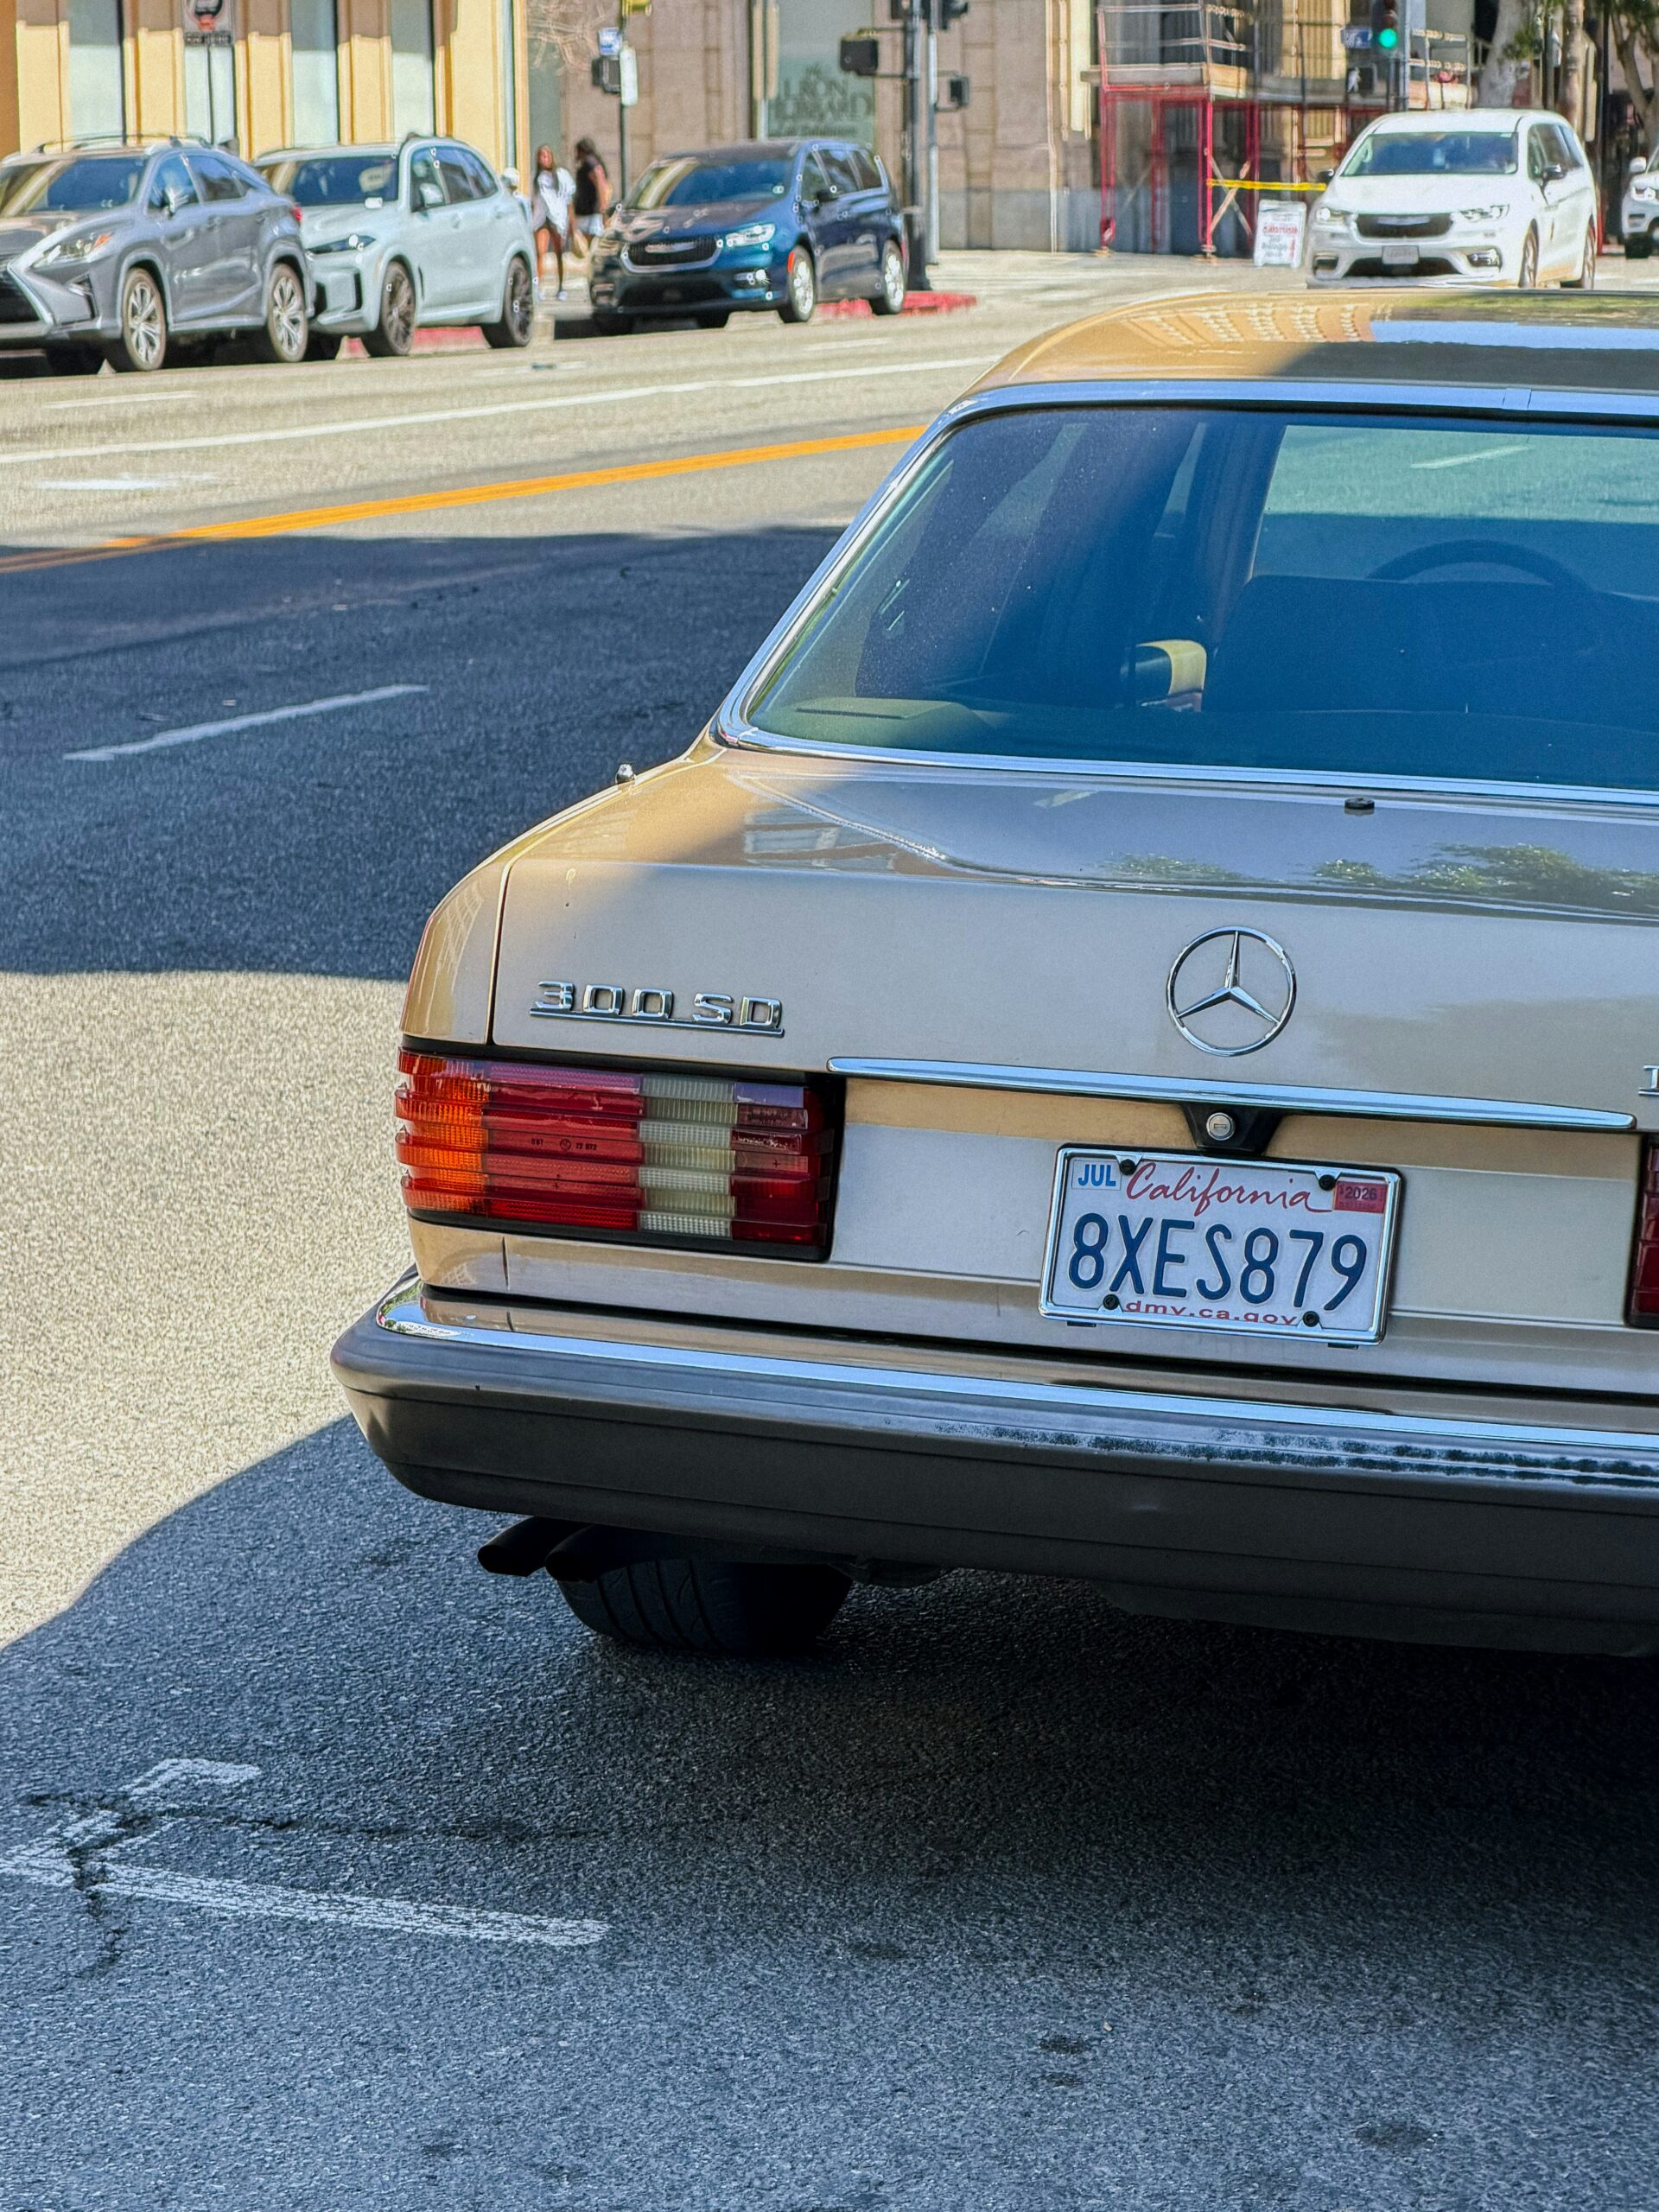
Senior United States District Judge William H. Orrick, sitting in the Northern District of California, denied a motion to dismiss last week in an Automated License Plate Recognition (“ALPR”) matter, McGinty v. Reimagined Parking LLC, d/b/a Imperial Parking.[1] Judge Orrick held that the plaintiff plausibly alleged actionable harm based on his “right to know” about the use of ALPR systems in two garages. The order follows Bartholomew v. Parking Concepts, Inc.[2] and the guidance of Mata v. Digital Recognition Network, Inc.,[3] concluding that the California Supreme Court would likely recognize violation of a consumer’s “right to know” as actionable harm under California’s ALPR law if presented with the question.

The decision is significant because it marks the first time a federal judge adopted the state-court trajectory created in Bartholomew and Mata. Bartholomew treated the alleged failure to make required ALPR disclosures in an ALPR Privacy Policy as an actionable injury to a consumer’s right to know under the law. Though Mata did not deal with the failure to present an ALPR Privacy Policy, the decision in Mata did offer further guidance on how courts should analyze asserted ALPR harms.

Continue Reading Federal Court Follows Bartholomew Reasoning in Denying Motion to Dismiss ALPR Lawsuit

On July 20, 2026, the California Court of Appeal, Fourth Appellate District issued a notable decision in Mata v. Digital Recognition Network, Inc.,[1] which addresses the standing requirements for private claims under California’s Automated License Plate Recognition (“ALPR”) law. At the heart of the decision lies the question whether a violation of the

Now in its sixth year, Seyfarth’s Commercial Litigation Outlook provides a clear view into the forces reshaping business disputes in 2026. This year’s analysis highlights a risk landscape defined by accelerating technological change, an increasingly fragmented regulatory environment, and growing economic pressures across multiple industries.

According to the Outlook, artificial intelligence is creating new categories of legal risk, from the challenges of authenticating AI‑generated content to navigating the use of algorithmic tools while courts and regulators rapidly reset expectations around emerging technology. At the same time, state‑level regulation continues to expand, particularly around non‑competes, privacy, and biometrics, creating a compliance patchwork that requires businesses to adapt strategies by jurisdiction. Coupled with elevated interest rates, rising debt, and post‑pandemic strain, especially in real estate, health care, and franchise sectors, the commercial litigation environment remains fluid, fast‑moving, and resistant to neat predictions. Against this backdrop, eDiscovery, information governance, and cybersecurity response functions play increasingly central roles in managing litigation risk and staying ahead of shifting expectations.


Authored by Jay Carle, Matthew Christoff, and Danny Riley, this year’s eDiscovery & Innovation article spotlights one of the most significant and fast‑moving risks in the discovery landscape: the rise of AI‑enabled notetaking and meeting‑summarization tools. As generative AI capabilities become embedded directly into videoconferencing platforms, these tools now routinely record meetings, create transcripts with speaker attribution, and auto‑generate summaries—often by default. The result is a sudden proliferation of new, unvetted records that can capture sensitive, strategic, or privileged conversations. The article warns that these tools exponentially increase the risk of inadvertent disclosure, while also creating evidentiary challenges when transcripts or summaries are later used to establish what was said, by whom, and with what intent.

The article also highlights that litigation risk is expanding beyond the developers of these tools to the organizations deploying them. AI notetakers raise overlapping consent, privacy, wiretap, and biometric concerns, and courts will increasingly scrutinize whether companies can demonstrate how meeting data was captured, stored, and controlled. As with prior waves of privacy litigation, the differentiator will be operational discipline: organizations that implement clear governance around meeting recording, restrict distribution of AI‑generated outputs, and define authoritative versions of records will be far better positioned to defend against disclosure missteps, authenticity disputes, and statutory claims.

Click here to download the 2026 Commercial Litigation Outlook.

Continue Reading The Changing Discovery Landscape: Takeaways from Seyfarth’s 2026 Commercial Litigation Outlook

This post was originally published to Seyfarth’s Global Privacy Watch blog.

California Senate Bill 690 (SB 690), introduced by Senator Anna Caballero, is continuing to proceed through the California state legislative process. The proposed bill would amend the California Invasion of Privacy Act (CIPA) by adding an exception to the statute which has the

Seyfarth Synopsis: In a significant decision for website operators, the Massachusetts Supreme Judicial Court clarified that tracking users’ web activity does not constitute illegal wiretapping under the state’s Wiretap Act. The court found that person-to-website interactions fall outside the Act’s scope, which focuses on person-to-person communications. However, the court emphasized that other privacy laws could

Corporations face unprecedented challenges in safeguarding sensitive data and mitigating privacy risks in an era marked by the rapid proliferation of Internet of Things, or IoT, devices.

Recent developments, including federal and state regulators’ heightened focus on privacy enforcement, highlight the importance of proactive risk management, compliance and data governance. As IoT and smart devices continue to hit the marketplace, heightened scrutiny for businesses’ data governance practices follows.

The Federal Trade Commission’s recent technology blog, “Cars & Consumer Data: On Unlawful Collection & Use”[1] underscores the agency’s commitment to enforcing consumer protection laws. Despite their blog’s focus on the car industry, the FTC’s message extends to all businesses, emphasizing its vigilance against illegal — or “unfair and deceptive” — collection, use and disclosure of personal data.

Recent enforcement actions are a stark reminder of the FTC’s proactive stance in safeguarding consumer privacy.

Geolocation data is a prime example of sensitive information subject to enhanced protections under the Federal Trade Commission Act. Much like mobile phones, cars can reveal consumers’ persistent, precise locations, making them susceptible to privacy infringements.

Continue Reading Careful Data Governance Is a Must Amid Enforcement Focus

On August 2, 2024, Illinois Governor J. B. Pritzker signed legislation reforming Illinois’ Biometric Information Privacy Act (BIPA). Senate Bill 2979 immediately amends BIPA to limit a private entities’ potential liability for collecting or sharing biometric data without consent.

The BIPA amendment followed a call for action  directed at the legislature from the Illinois courts.

This post was originally published to Seyfarth’s Global Privacy Watch blog.

On July 10th, the European Commission issued its Implementing Decision regarding the adequacy of the EU-US Data Privacy Framework (“DPF”). The Decision has been eagerly awaited by US and Europe based commerce, hoping it will help business streamline cross-Atlantic data transfers, and by

Seyfarth Synopsis: The U.S. District Court for the Northern District of Illinois recently denied Plaintiff’s motion to reconsider a prior dismissal of his privacy action due to untimeliness.  In a case titled Bonilla, et al. v. Ancestry.com Operations Inc., et al., No. 20-cv-7390 (N.D. Ill.), Plaintiff alleged that consumer DNA network Ancestry DNA violated the